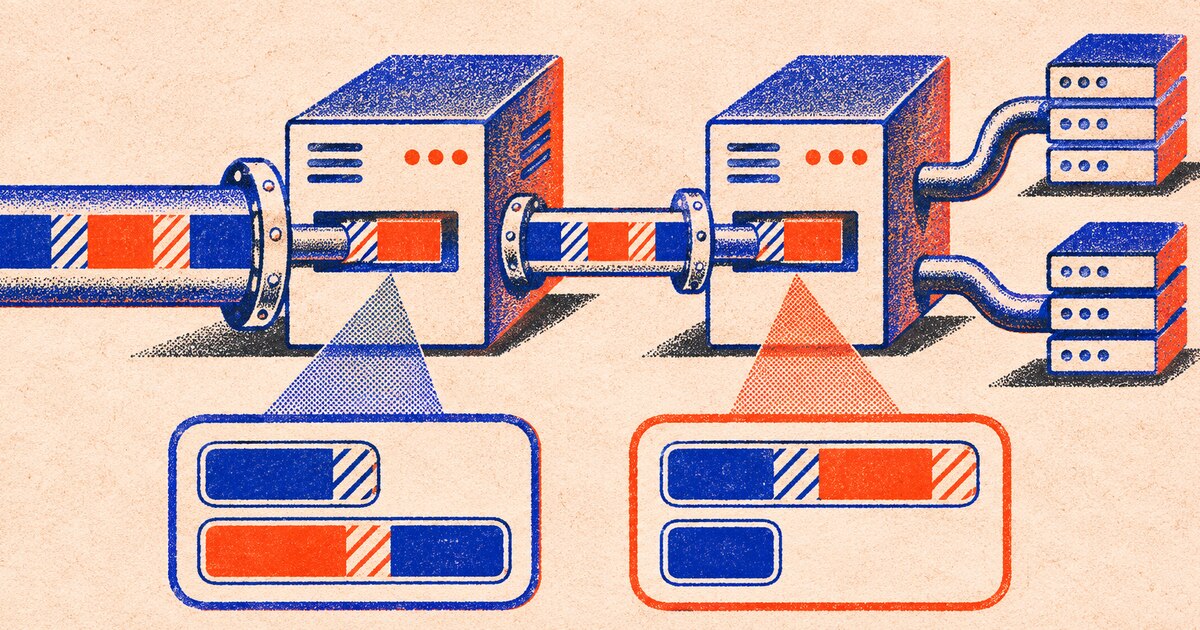
Hello everyone. HTTP request smuggling was a difficult topic for me to learn, so I worked through several articles, videos, and other resources. In this article, I'll explain it in plain English and finish with references and tools. ;)
Let's begin and cover the basics in one article.
# What is HTTP Request Smuggling?
HTTP request smuggling is a technique for interfering with the way a web site processes sequences of HTTP requests that are received from one or more users. Request smuggling vulnerabilities are often critical in nature, allowing an attacker to bypass security controls, gain unauthorized access to sensitive data, and directly compromise other application users.
~https://portswigger.net
HTTP request smuggling is also called an HTTP desync attack because the front-end and back-end servers interpret the same request differently, producing an unexpected response or error. That is the basic idea behind request smuggling.
To understand request-smuggling behavior, we first need to understand the specifications that shape it. The original article referenced RFC 2616, which is now obsolete; current HTTP/1.1 message framing is specified in RFC 9112. The historical quotation below is retained for context.
# Core Concept
Historical reference: RFC 2616 (obsolete)
If a message is received with both a Transfer-Encoding header field and a Content-Length header field, the latter MUST be ignored.
Content-Length
The Content-Length entity header indicates the size of the entity-body, in bytes, sent to the recipient.
Transfer-Encoding: chunked
The Transfer-Encoding header specifies the form of encoding used to safely transfer the payload body to the user.
Chunked means that large data is sent in a series of chunks
Front-End Server (Load Balance | Reverse Proxy)
Process the content-length
Back-End Server
Process the transfer-encoding
Carriage Return Line Feed (CRLF) \r\n
You check out my previous blog about CRLF if any confusion in what is CRLF.
But here CRLF characters play vital role in request smuggling as they append in end and they are also not visible in the request.
\r = 1 byte, \n = 1 byte
Size: (in bytes)
Will come into play when performing it manually [It can be tricky]:)
# How this Issue is caused? (Laymen-term)
When a request arrives, the front-end server processes the content-length while the back-end server processes the transfer-encoding and the two servers therefore interpret the same request differently. They can fall out of sync and produce an unexpected response, causing request smuggling.
Vulnerabilities exploited via Request Smuggling:
- XSS
- Unauthenticated Access
- Web Cache Poisoning
- Web Cache Deception
# Understanding Transfer-Encoding
We'll understand it with the help of an Image.
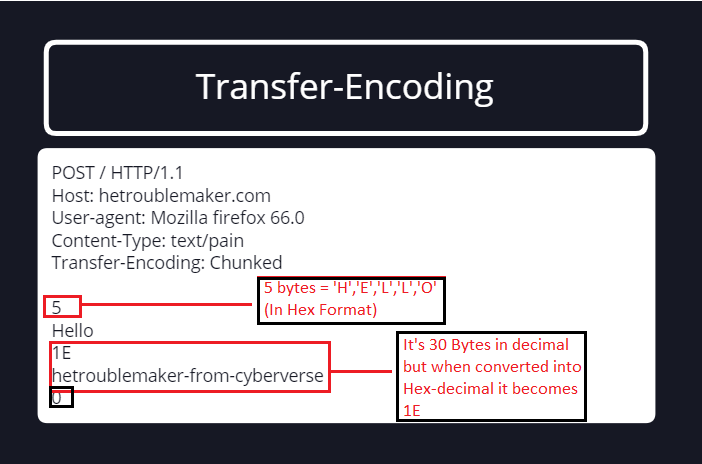
Here in this above image Transfer encoding is used and you can see chunked is also used which sends the large data into chunk series.
Key Points:
5: tells that Hello has 5 character in Hexa-Decimal (5 Decimal = 5 Hex)
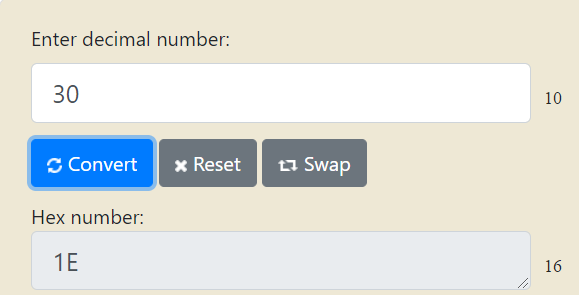
1E: tells that hetroublemaker-from-cyberverse has 30 character in Hexa-Decimal
0: in the end it tells to terminate the request( Termination-Point)
#Understading Content-Length
We'll understand it with the help of an Image.
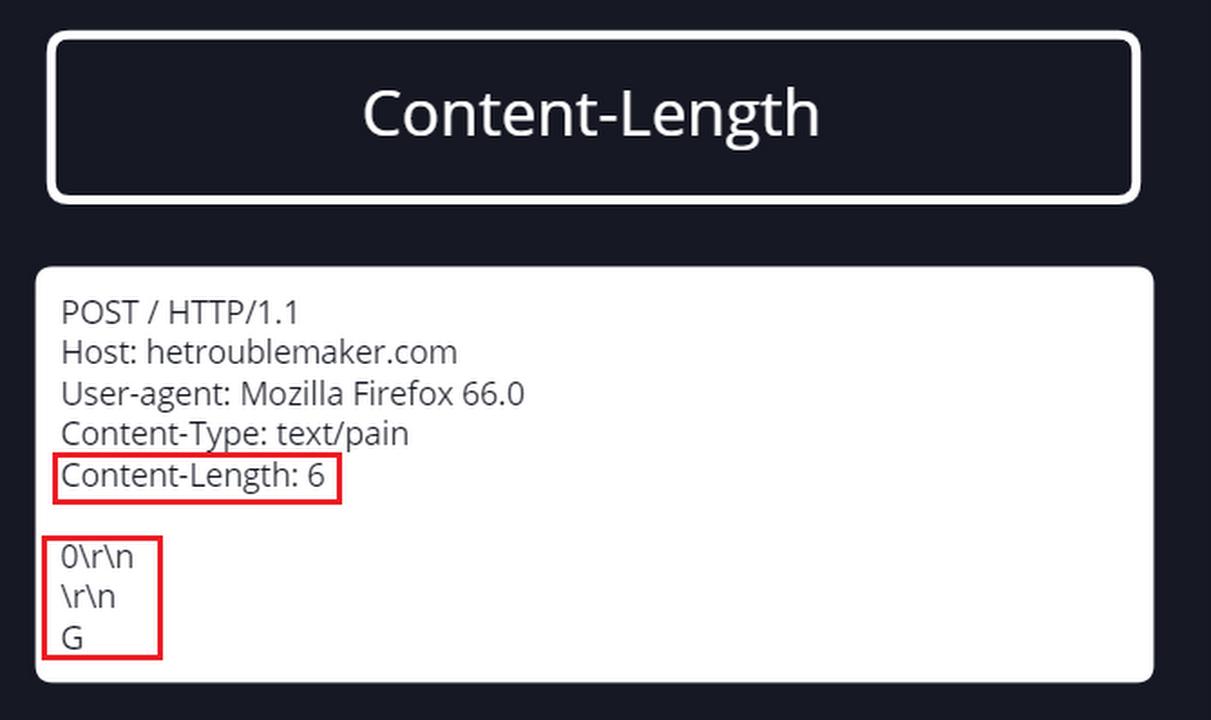
The Content-Length is 6, which confused me at first. In a real request, the CRLF characters are not visible, but they appear after each line and count toward the request body length. Therefore, 0 + \r + \n + \r + \n + G = a Content-Length of 6.
# Now, it's time to Understand the Actual Vulnerability.
1. CL.TE (Content-length.Transfer-encoding)
Let's take an example here and understand with an Image:
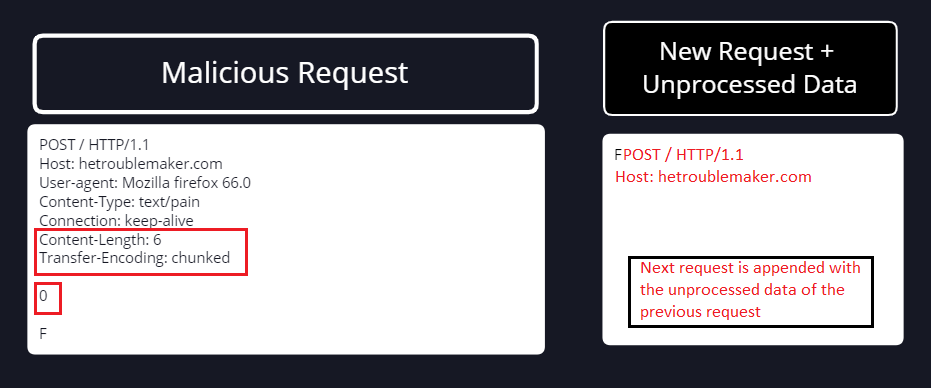
As you can see in the above image Content-Length & Transfer-Encoding both are used and According to RFC specifications if both the headers are present in a single request then they will conflict each other and then the Content-Length header should be ignored.
Now, let's suppose if the front-end server processes the content-length then it'll check the Content-Length header of the Request which is equal to 6. (0+(CRLF characters)+F) = 6
After front-end, the request will go to back-end server and here Transfer-Encoding comes into play; As you know back-end processes the T.E, So it'll check for Transfer-Encoding header and also we have mentioned 0 'Zero' (which means Termination Point). And If back-end supports T.E it'll not forward the rest of data after it's termination point and "F" will remain unprocessed until next request. And will append with the Next Request as you can see in the above image [Request in red in the next request]
DEMO:
2. TE.CL (Transfer-Encoding.Content-Length)
Here, the front-end server uses the Transfer-Encoding header and the back-end server uses the Content-Length header.
Let's understand it with an Image.
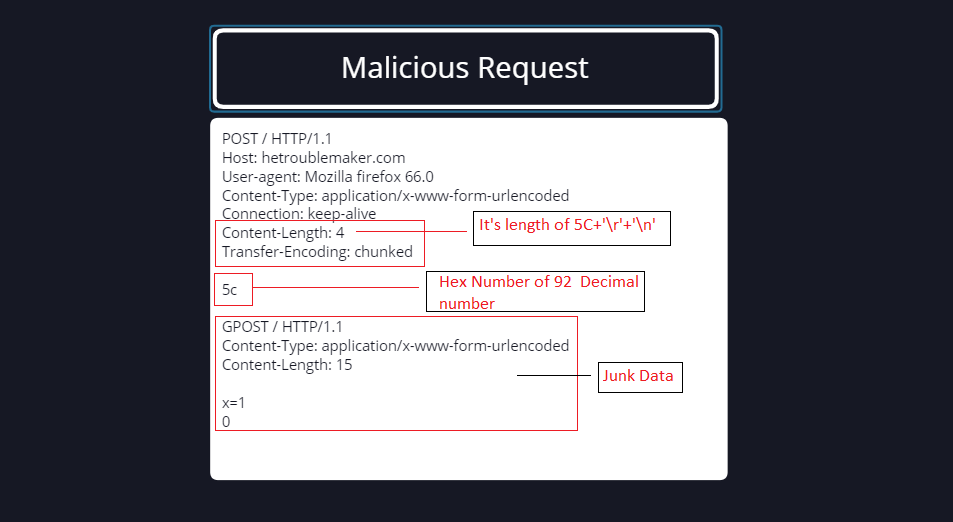
Here, the malicious request contains Transfer-Encoding: chunked & Content-Length: 4. Now analyze the request: Content-Length is 4 because it covers 5c plus the CRLF characters; 5c is the hexadecimal representation of decimal 92. The remaining junk data is left unprocessed, and the back-end server treats it as the start of the next request in the sequence.
DEMO:
#There is also TE.TE vulnerability which I expect you can do it on your own :D
# Some Automation
- Burp suite's extension: HTTP Request Smuggler
GitHub - PortSwigger/http-request-smuggler
2. This is a tool created by Gwendal Le Coguic
DEMO:
THE END
Before finishing, I'll share several useful articles and HackerOne reports about HTTP request smuggling.
- Help you understand HTTP Smuggling in one article
- Escalating reflected XSS with HTTP Smuggling
- Slack disclosed on HackerOne: Mass account takeovers using HTTP...
- Lob disclosed on HackerOne: HTTP Request Smuggling on vpn.lob.com
- New Relic disclosed on HackerOne: Password theft login.newrelic.com...
- Write up of two HTTP Requests Smuggling
Those are the basics of request smuggling. I hope this explanation made the topic easier to understand.
So, Until Next Blog
Best of luck everyone. Keep-Hacking!
Feedback and corrections are welcome.
If this article helped, share it with another researcher who might find it useful.
From research to a scoped assessment.
Explore Web application penetration testing or browse the full Bug Bounty Archive for more evidence-focused research.
Research topics: security / hetroublemaker / http-request / hacking / bug-bounty