Hi everyone. I'd like to start with a question: what was the first vulnerability you learned about when you began studying cybersecurity?
Mine was XSS. It took me quite a while to find one, but I finally did. (shrug)
Case Study
I received an invitation to a private HackerOne program that already had more than 600 reports across only four assets. I wondered whether I would find anything.
I still began with my usual reconnaissance and started testing the application. At first, I had no luck.
Next, I started mining parameters. Here is the workflow: these were the tools and techniques I used.
Cihan Mehmet DOGAN (CMD) on Twitter
@marcolivermunz @hahwul you can use it as below. gospider -S tageturls.txt -c 10 -d 5 --blacklist ".(jpg|jpeg|gif|css|tif|tiff|png|ttf|woff|woff2|ico|pdf|svg|txt)" --other-source | grep -e "code-200" | awk '{print $5}'|grep "=" | qsreplace -a | dalfox pipe -o result.txt
- GitHub - s0md3v/Arjun: HTTP parameter discovery suite.
- GitHub - hakluke/hakrawler: Simple, fast web crawler designed for easy, quick discovery of endpoints and assets within a web application
You can also use "Waybackurls | gau" to find parameters. These were useful techniques in my workflow, and the results were strong. (shrug)
With the parameter list ready, I began fuzzing in the hope of finding something interesting (Positive Vibes) and found a parameter with few filters. Because this was my first time testing for XSS, I sent it to a couple of XSS scanners first.
- GitHub - s0md3v/XSStrike: Most advanced XSS scanner.
- GitHub - hahwul/dalfox: Dalfox is a powerful open-source XSS scanner and utility focused on automation.
The tools returned positive results, and I found a csrfToken exposed there. :P
https://sub.example.com/?csrfToken=htmhunter
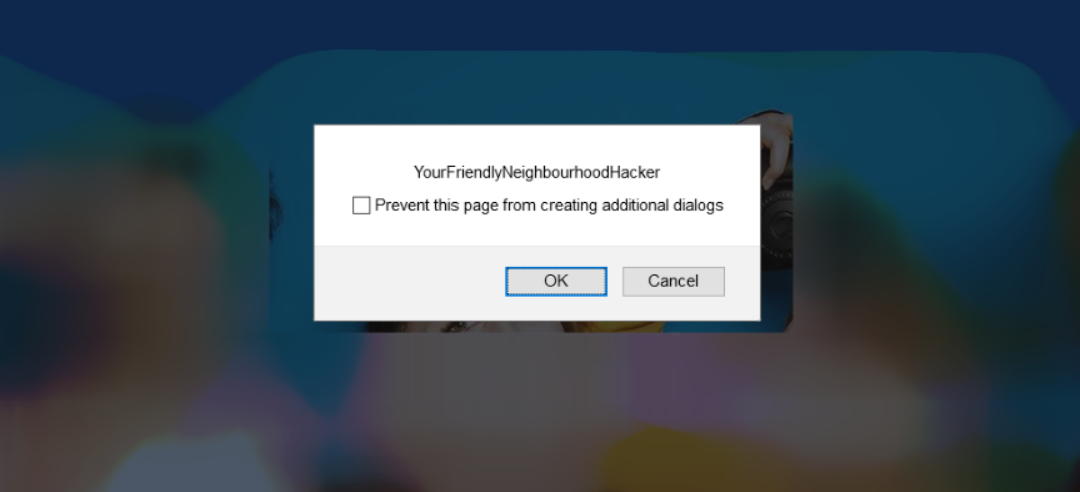
I then explored how to trigger the alert.
Later that day, I reported my first XSS on HackerOne.
Takeaways:
Don't let an old program or a high report count discourage you. Keep discovering parameters and test them methodically. :D
That's all for this blog. Hope you liked it.
Connect with me on LinkedIn, Twitter
If this article helped, share it with another researcher who might find it useful.
From research to a scoped assessment.
Explore Web application penetration testing or browse the full Bug Bounty Archive for more evidence-focused research.
Research topics: security / hetorublemakr / bug-bounty / xs / hacking