Hello guys, I recently encountered an amazing bypass to change my Phone Number in an application that doesn’t allow anyone to change its Phone number after registration. An Easy Win!
Case Study
As this was a private program all illustrations of vulnerabilities will be represented with the host as redact.com
The application had a Registration page where a user could register a new username and password which allowed him to log in to the application via the login page.
While doing the registration. In the end, the web application sends an OTP to the phone number to verify it. Till now it was all normal like every other application.
When opened “My Account”. It looked like this
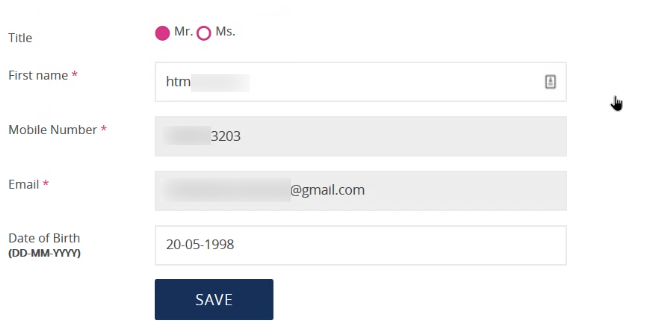
And looked like every other account info page with not many options available, like as you can see email address and Mobile number options are disabled by default.
And I started playing with it, I opened Inspect Element and changed the value of Mobile Phone from ******3203 to ******3213
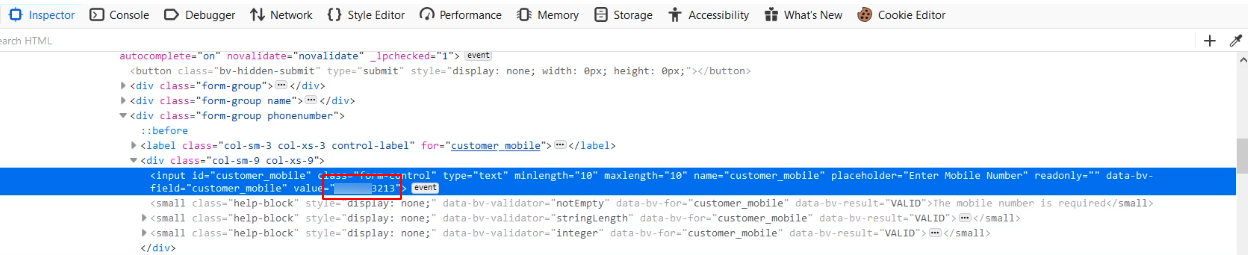
and click “SAVE” and it said Updated Successfully!!

So to confirm that does it really changed my Mobile number? I reloaded the page again and my Mobile Number has been changed successfully which does not belong to me and I didn’t even verify it.
Reported: 15 Jan’19
Responded: 18 Jan’19
Rewarded: 22 Jan’19
Takeaways –
Always try to check and change the value which is disabled by default and save the changes, it is possible that it remains changed.
That’s all for this blog. Hope you liked it.
From research to a scoped assessment.
Explore When validation rules belong on the server or browse the full Bug Bounty Archive for more evidence-focused research.
Research topics: hetroublemakr / rewards / security / hacking / bug-bounty