Hello everyone. I found a simple bypass that let me change my phone number in an application that did not allow users to change it after registration.
Case Study
Because this was a private program, every example uses redact.com as the placeholder host.
The application had a Registration page where a user could register a new username and password which allowed him to log in to the application via the login page.
At the end of registration, the web application sent an OTP to verify the phone number. Up to this point, the flow looked normal.
When opened "My Account". It looked like this
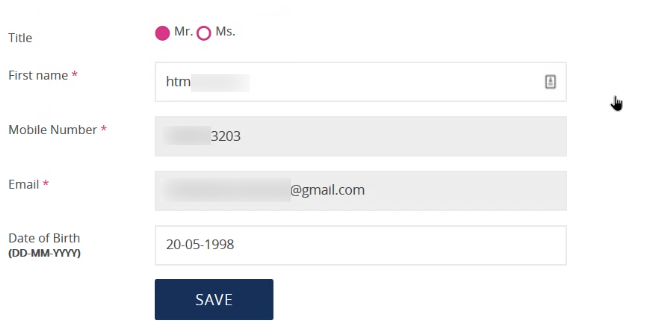
It looked like a typical account information page with few options. As shown below, the email address and mobile number fields were disabled by default.
I opened Inspect Element and changed the mobile phone value from ******3203 to ******3213
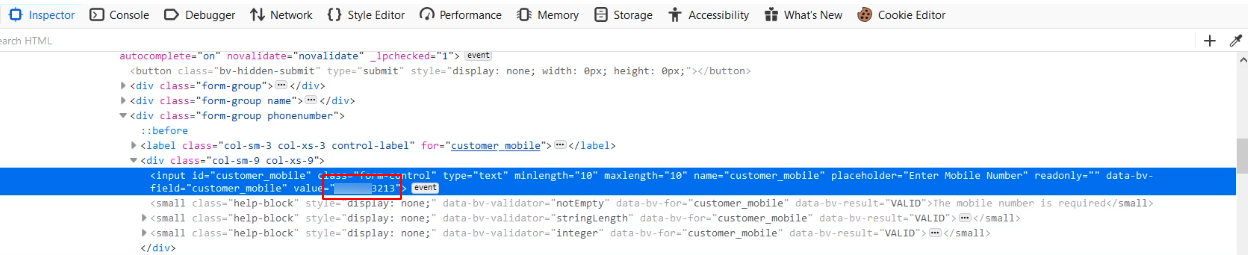
and click "SAVE" and it said Updated Successfully!!

To confirm whether the change had worked, I reloaded the page. My mobile number had been changed successfully, even though the new number did not belong to me and I had not verified it.
Reported: 15 Jan'19
Responded: 18 Jan'19
Rewarded: 22 Jan'19
Takeaways:
Always check whether a value that is disabled in the interface can still be changed and saved. The server may accept it without enforcing the same restriction.
That's the full case study. I hope it was useful.
From research to a scoped assessment.
Explore When validation rules belong on the server or browse the full Bug Bounty Archive for more evidence-focused research.
Research topics: hetroublemakr / rewards / security / hacking / bug-bounty